TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Security company Apiiro reports finding passwords and other secrets in 1,122 public GitHub files linked to Claude Code’s “Don’t Ask Again” permission setting. The report identifies a potential pattern involving coding-agent configuration, but the supplied material does not establish whether credentials remain valid, how many distinct users are affected, or whether Anthropic has responded.
Security firm Apiiro says it found passwords and other secrets in 1,122 public GitHub files associated with Claude Code’s “Don’t Ask Again” permission setting, raising concerns about sensitive information being committed to public repositories during AI-assisted software development. The supplied report extract does not show how Apiiro gathered or verified the files, or whether the exposed credentials remain usable.
Apiiro’s report, titled “Coding Agents Leaking Secrets: GitHub ‘Don’t Ask Again,’” connects the files to Claude Code, Anthropic’s coding assistant, and its permission interaction. The company characterizes the issue as secrets being exposed in public GitHub files. The headline count is 1,122 files; that figure should not be read as 1,122 unique passwords, accounts, or affected developers, since the available material does not provide those breakdowns.
The source material provided for this article contains the report’s title and a large amount of Apiiro website navigation and product text, but not the report’s underlying technical findings. It therefore does not specify the file types or repository history involved, the kinds of credentials identified, the time period covered, or how many files may have contained duplicates. No methodology, sample, or independent validation is included in the supplied excerpt.
There is also no source material here confirming whether the files were removed, whether credential owners were notified, or whether Anthropic has changed Claude Code’s behavior. The reported count is attributable to Apiiro; broader claims about the cause, scale of harm, or current exposure cannot be established from the excerpt alone.
Risks of Committing Agent Settings
Publicly exposed credentials can give outsiders access to services or systems if the secrets are active and provide sufficient permissions. If developers store credentials in files that are committed to a public repository, those secrets may remain discoverable even after a file is deleted, depending on repository history and whether copies have been made. Apiiro’s report points to a practical security concern for teams using coding agents: permission choices and generated or edited project files need to be reviewed before they are shared.
The report does not establish that any listed credential was used to access an account, that a breach occurred, or that the software itself leaked the values. Those distinctions matter. The number of files is a signal to investigate, not a measure of confirmed victims or resulting damage. For users and organizations, the immediate relevance is checking public repositories and treating any potentially exposed, still-valid secret as requiring assessment and possibly revocation.
Products Worth Considering

Trezor Safe 7 Crypto Hardware Wallet with Bluetooth and Color Touchscreen

Logitech MX Keys Combo for Business Keyboard and Mouse – Graphite
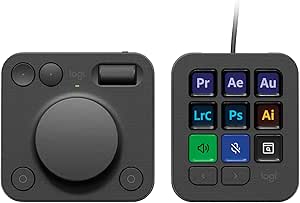
Logitech MX Creative Console with 9 Customizable Keys, Graphite
As an affiliate, we earn on qualifying purchases.
How the Setting Relates to Exposure
Claude Code is an AI coding tool that can interact with a developer’s working environment, while “Don’t Ask Again” is the permission-related wording identified in Apiiro’s report title. The headline links that setting to secrets appearing in public GitHub files, but the material supplied does not explain the precise sequence that produced those files or show whether a user action, configuration choice, or software behavior was responsible.
That distinction is necessary for understanding the finding. A credential appearing in a repository may result from several points in a development workflow, including a file being created or edited and later committed. The source excerpt does not document which of those steps occurred in the files Apiiro counted, so the setting’s role should be described as the report’s association rather than a demonstrated technical cause.
““Coding Agents Leaking Secrets: GitHub ‘Don’t Ask Again’””
— Apiiro, in the report title
Scope and Credential Status Unverified
The available source material does not identify the credentials, name affected repositories, or state whether the files were checked for validity. It also does not explain the search method, the dates covered, how duplicates were handled, or whether each file was tied to the same setting in a technically verified way. As a result, the reported 1,122-file count cannot be converted into a count of distinct exposed accounts or confirmed security incidents.
No response from Anthropic, affected repository owners, or GitHub appears in the supplied material. It remains unclear whether any credentials are still publicly accessible, whether they have been revoked, and whether the finding reflects a continuing behavior or files created under earlier versions of the tool. Those points would be needed to assess the present risk and determine responsibility.
Verification and Remediation Needed
The next steps for establishing the scope are publication or review of Apiiro’s full technical methodology, verification of the identified files, and clarification of whether the count represents unique secrets and repositories. A response from Anthropic could clarify how the permission setting operates and whether any product changes or guidance are planned. The supplied material does not state that such a response or update has been announced.
Developers and organizations that may be affected can check public repositories for credentials, revoke or rotate any secrets confirmed to be exposed, and review repository history and access logs. These are general defensive measures, not confirmation that a particular account was compromised. Until the findings and credential status are independently clarified, the reported figure should be treated as Apiiro’s count of files rather than a verified tally of active passwords or affected users.
Key Questions
What did Apiiro report?
Apiiro says it found 1,122 public GitHub files containing passwords or other secrets associated with Claude Code’s “Don’t Ask Again” setting. The supplied report excerpt does not include the underlying file list or technical method.
Does the number mean 1,122 people were affected?
No. The reported figure counts files, and the source material does not say how many unique credentials, accounts, repositories, or developers those files represent.
Are the exposed passwords still valid?
The supplied material does not say whether the credentials were tested, remain active, or have been revoked. Their current status is unverified.
Has Anthropic confirmed the issue or changed Claude Code?
No Anthropic response or product change is included in the source material provided. Whether the company has commented or taken action is not established here.
What should developers do if they find a credential in a public repository?
They should treat a confirmed exposed credential as potentially compromised, revoke or rotate it, and review relevant access logs and repository history. The report excerpt does not identify particular repositories or accounts to check.
Source: apiiro.com