TL;DR
Security experts are urging organizations to focus on authorization rather than authentication to improve access control. The shift aims to enhance security and streamline user management, but implications are still being evaluated.
Cybersecurity professionals are increasingly advocating for a shift in security approach: prioritizing authorization over authentication to better control access to digital resources. This emerging perspective challenges traditional security models and could influence future industry standards.
Recent industry discussions, highlighted in a series of expert panels and technical papers, emphasize that authorization—the process of granting specific permissions—should take precedence over authentication—the verification of user identity—when designing access controls. Learn more about email security standards like DMARC. Advocates argue that this focus reduces vulnerabilities associated with identity verification failures and streamlines user experience.
Leading voices, including cybersecurity researchers and enterprise security officers, suggest that implementing authorization-centric frameworks can mitigate risks posed by compromised credentials and simplify policy enforcement across complex systems. See how DMARC can help protect your domain from email fraud. However, some experts caution that this approach requires a fundamental rethinking of current security architectures and may not be suitable for all contexts.
Implications for Security Strategies and Industry Standards
This shift towards prioritizing authorization over authentication could significantly impact how organizations design their security systems. It may lead to more resilient access controls that are less dependent on verifying identities, thereby reducing the risk of credential theft and impersonation. Nonetheless, the approach raises questions about how to ensure secure, user-specific permissions without robust identity verification, and whether current compliance frameworks can adapt to this paradigm shift.
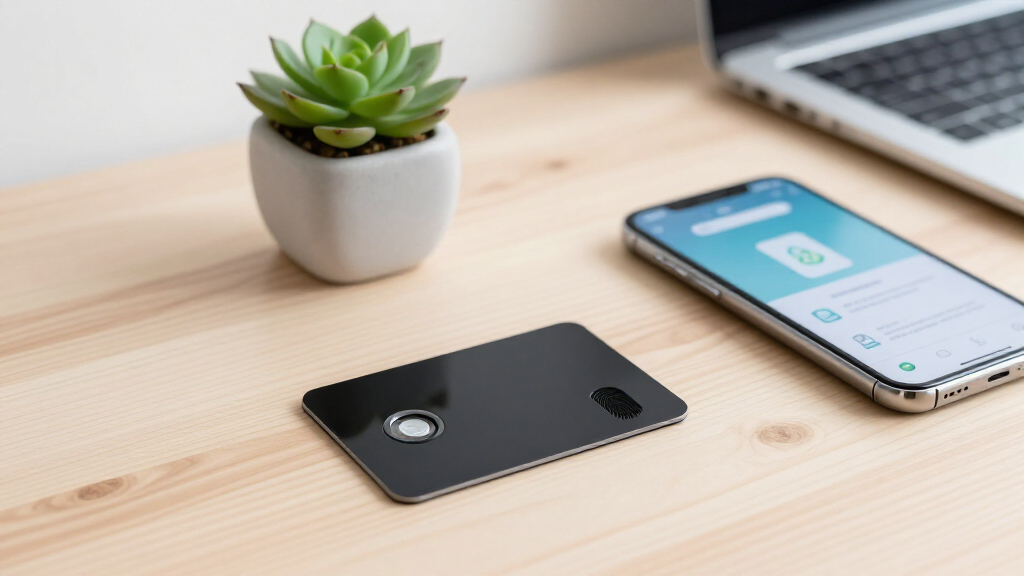
hardware security keys for access control
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Evolution of Access Control Practices in Cybersecurity
The traditional security model relies heavily on authentication—such as passwords, biometrics, and multi-factor verification—to confirm user identities before granting access. Over recent years, security breaches involving credential theft and phishing attacks have prompted experts to reconsider this reliance. The emerging emphasis on authorization reflects a desire to minimize damage by controlling what users can do once access is granted, regardless of how their identity was verified.
This debate is part of a broader trend toward zero-trust security architectures, which assume that threats can exist both inside and outside the network. The principle of authorize, don’t authenticate is gaining traction as a way to implement more flexible, resilient access policies that adapt to evolving threat landscapes.

Yubico – YubiKey 5C NFC – Multi-Factor authentication (MFA) Security Key and passkey, Connect via USB-C or NFC, FIDO Certified – Protect Your Online Accounts
- Security Type: Multi-Factor Authentication (MFA)
- Compatibility: Works with 1000+ accounts
- Connection Options: USB-C and NFC
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Unresolved Questions About Implementation and Effectiveness
It remains unclear how organizations will balance authorization with authentication to maintain security and compliance. Specific frameworks and standards for adopting this approach are still under development, and industry consensus has yet to be reached. Additionally, the effectiveness of authorization-first models in preventing sophisticated attacks is still being evaluated through ongoing pilot projects.
enterprise authorization management tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Expected Developments and Industry Adoption Timeline
Security vendors and standards organizations are likely to release new guidelines and tools to support authorization-focused security architectures in the coming months. Organizations are encouraged to monitor pilot results and consider phased implementations. Further research and case studies will clarify best practices for integrating authorization as the primary security control.
As an affiliate, we earn on qualifying purchases.
Key Questions
Authentication verifies a user’s identity, while authorization determines what actions or resources the user is permitted to access after their identity is confirmed.
This approach aims to reduce reliance on potentially vulnerable identity verification methods and focus on controlling what users can do once access is granted, thereby improving overall security resilience.
Yes, if not properly managed, it could lead to unauthorized actions if permissions are not accurately assigned. Balancing security and usability remains a key challenge.
Is this approach suitable for all types of organizations?
Not necessarily; smaller or less complex environments may still rely heavily on authentication. Larger, more dynamic systems might benefit more from an authorization-first strategy, but implementation details vary.
When can we expect industry standards to adapt to this shift?
Standards organizations are beginning to explore this paradigm, but widespread adoption and formal guidelines may take several years as best practices are established through ongoing research and real-world testing.
Source: hn