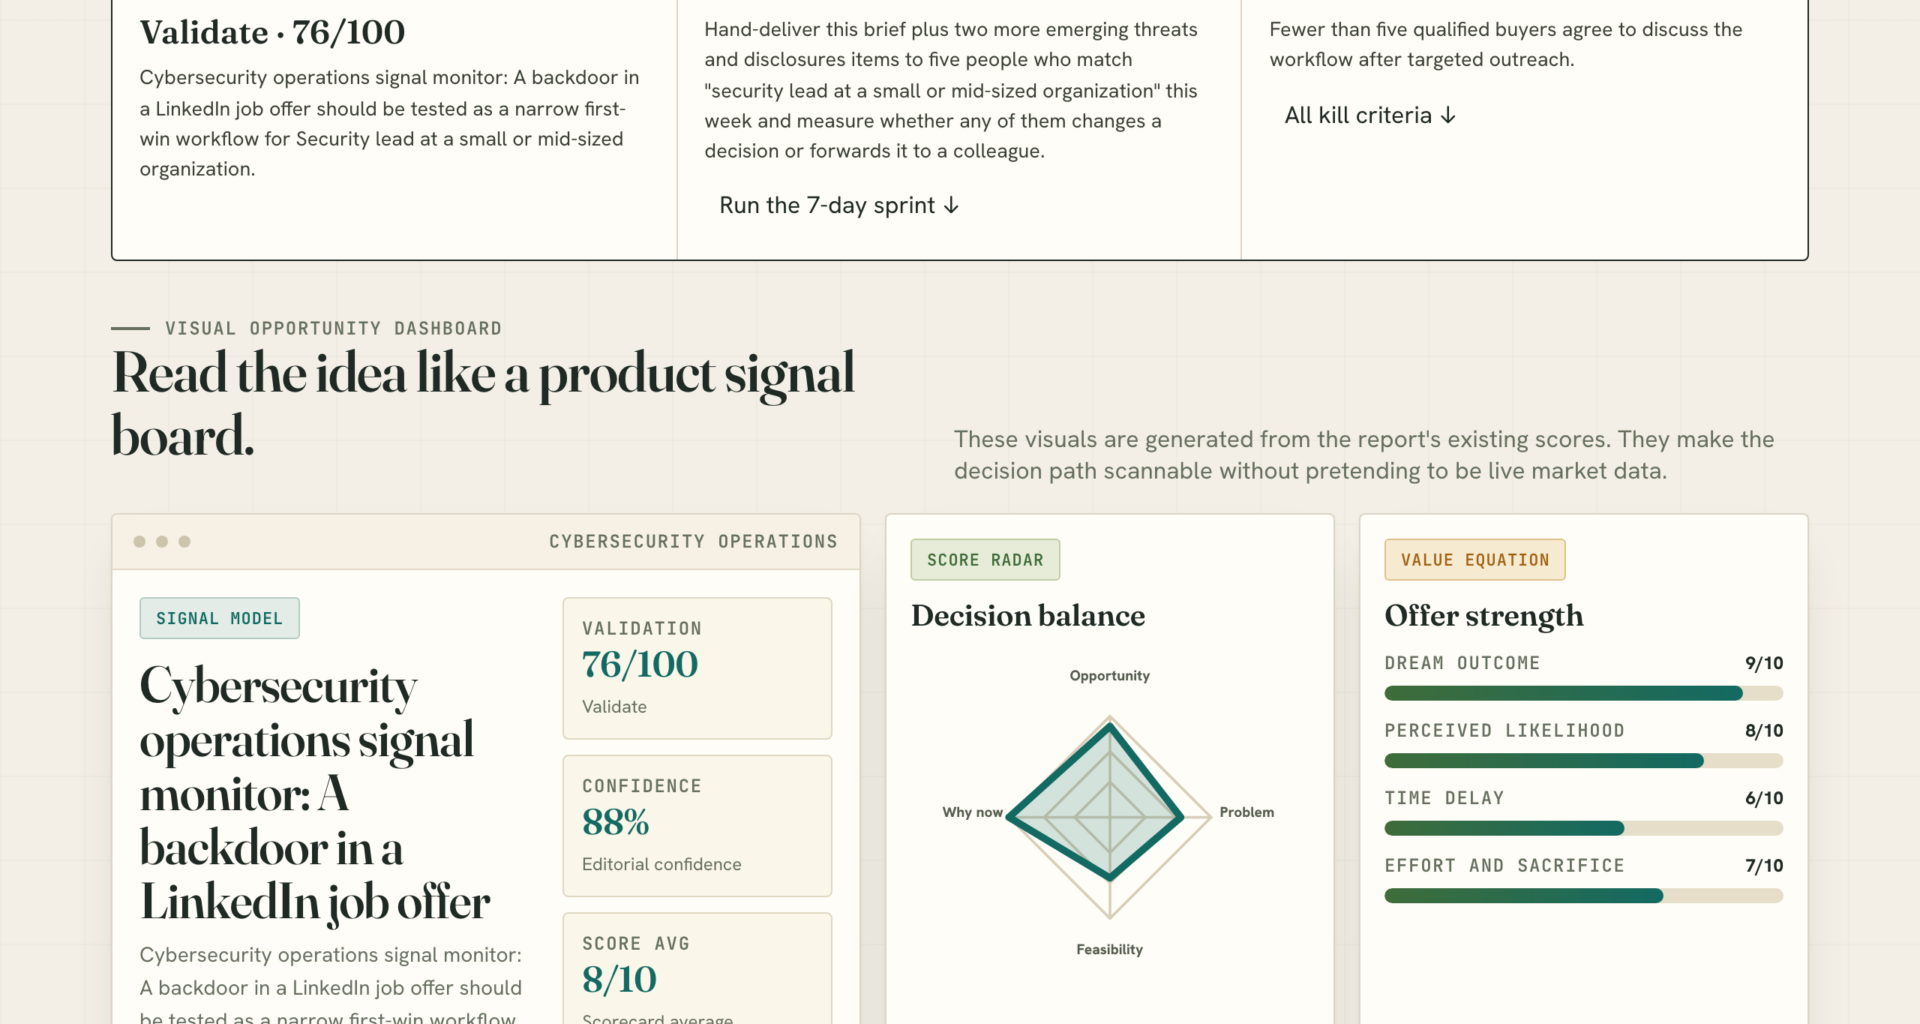
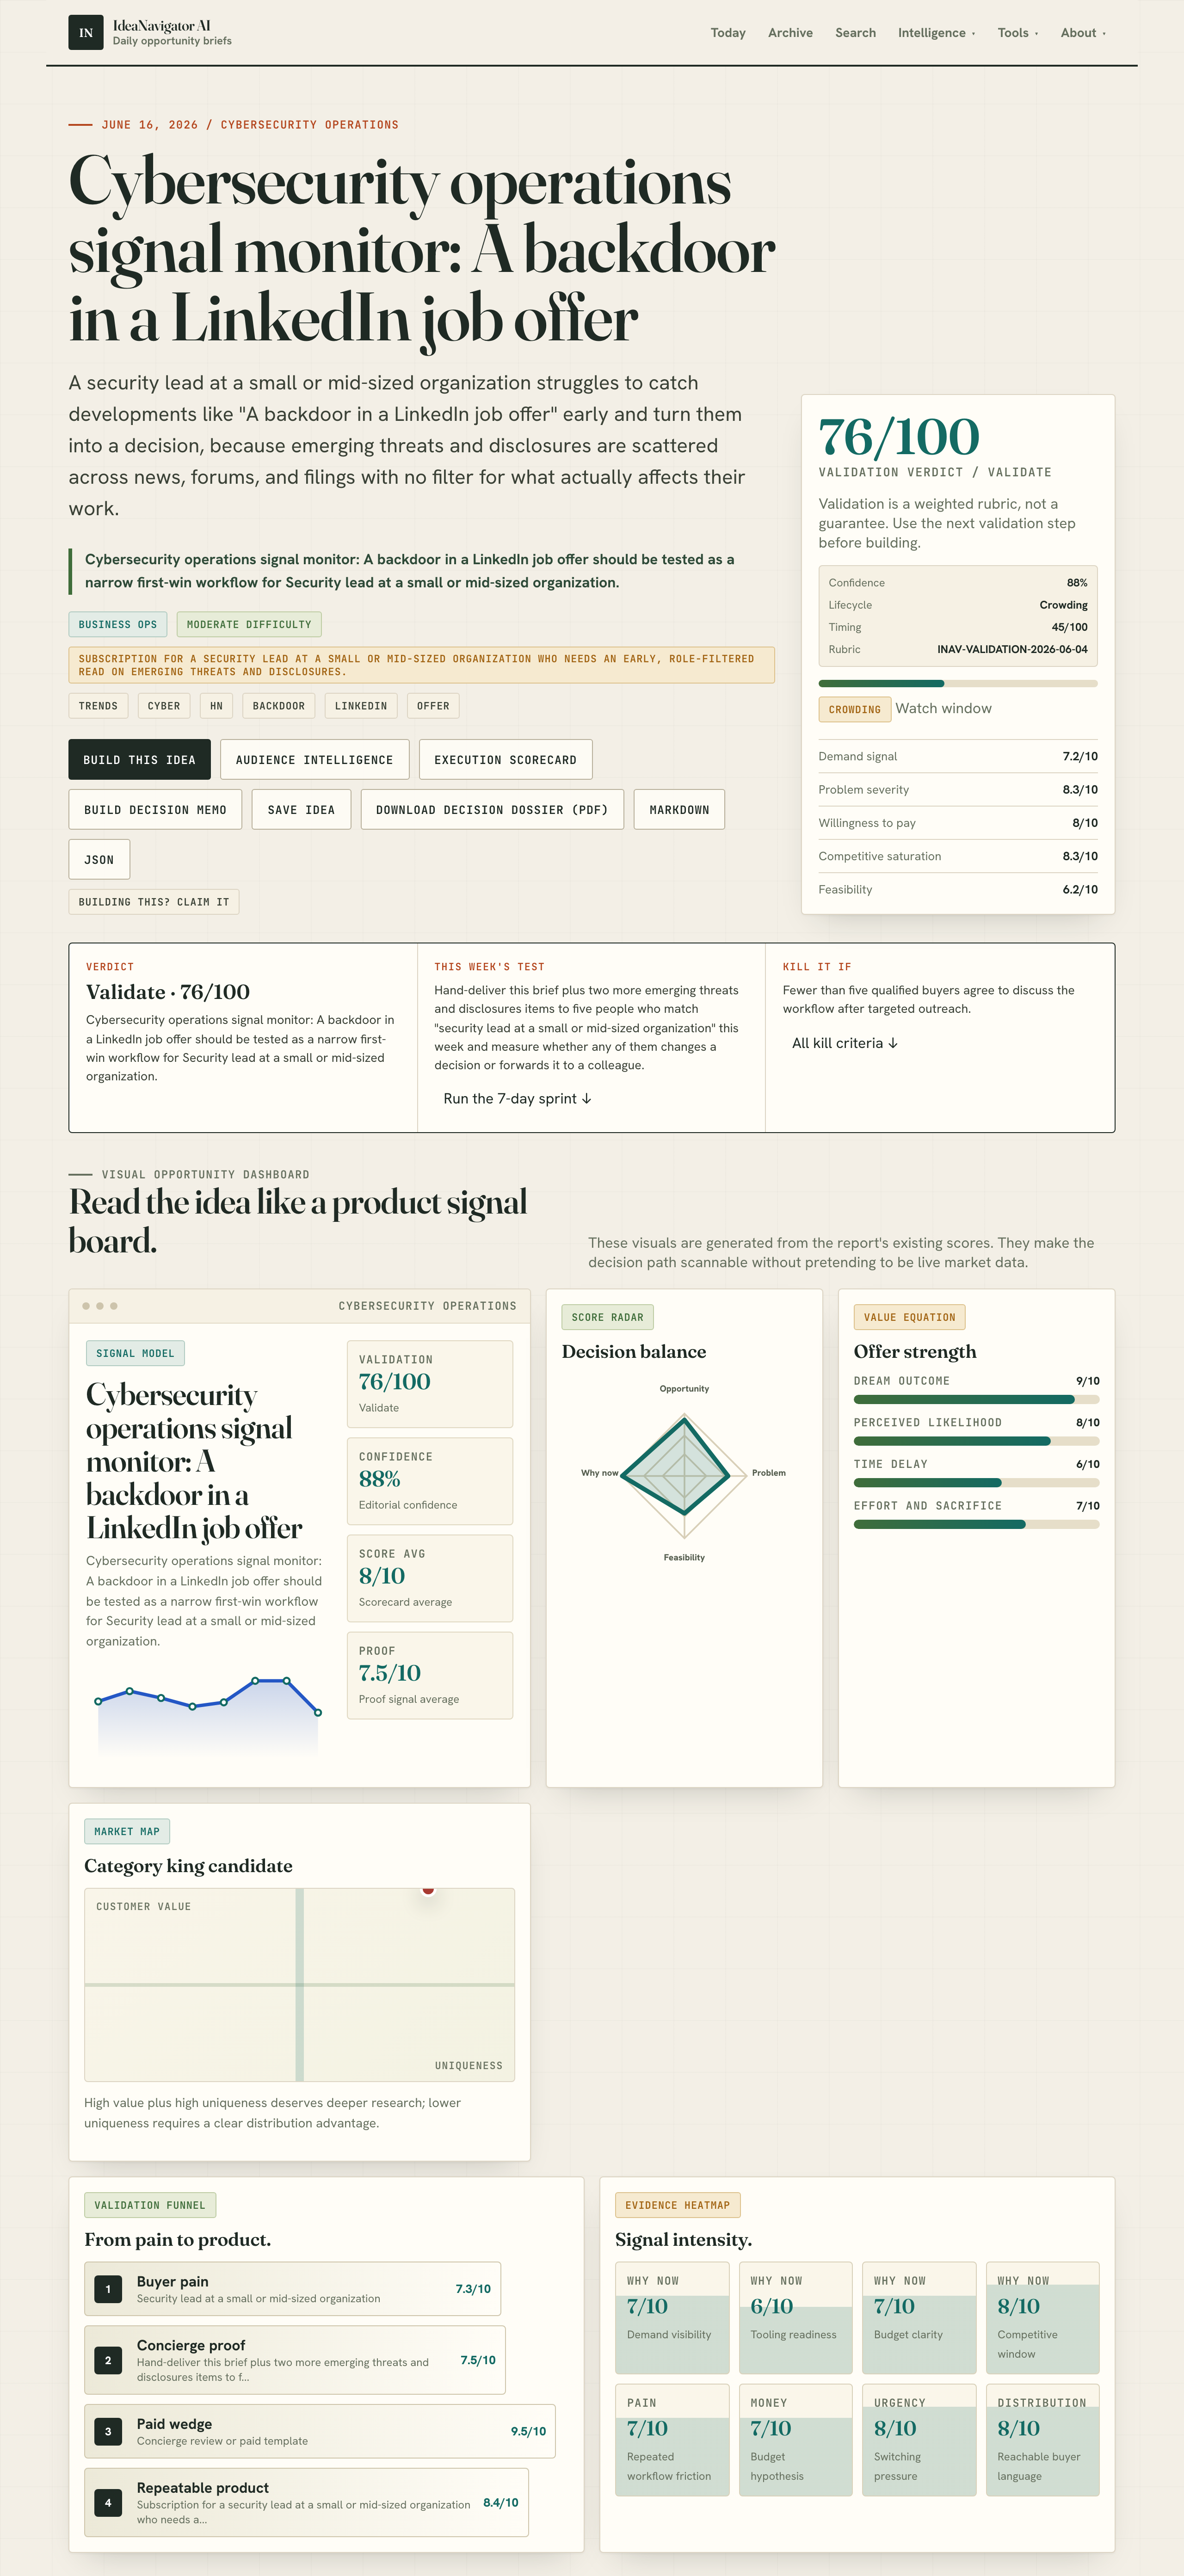
📊 Full opportunity report: Cybersecurity operations signal monitor: A backdoor in a LinkedIn job offer on IdeaNavigator AI — validation score, market gap, and execution plan.

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
Cybersecurity analysts have confirmed the discovery of a backdoor in a LinkedIn job offer. This development underscores evolving threats in online job scams and emphasizes the need for vigilance among security leaders.
Cybersecurity analysts have confirmed the presence of a backdoor embedded in a LinkedIn job offer, posing a new threat vector for organizations and job seekers alike. This discovery, made by cybersecurity teams monitoring emerging online threats, underscores the increasing sophistication of cybercriminal tactics targeting recruitment platforms.
The backdoor was identified through cybersecurity operations monitoring signals on platforms like Hacker News. It involves malicious code embedded within a seemingly legitimate LinkedIn job posting, which could potentially allow unauthorized access to targeted systems or data once interacted with by a candidate or recruiter.
Experts emphasize that this threat is part of a broader trend of cybercriminals exploiting online job listings to deploy malware or gain initial footholds in organizational networks. The specific technical details of the backdoor are still under analysis, and no confirmed cases of exploitation have been publicly reported yet.
Implications for Small and Mid-Sized Organizations
This development highlights the growing risks associated with online recruitment scams, especially for smaller organizations that may lack advanced detection capabilities. The backdoor’s potential use for initial access underscores the importance of vigilance in vetting online job offers and monitoring for malicious activity.
Security leaders should consider reviewing their threat detection protocols and educating HR and hiring teams on spotting suspicious postings. The incident also signals a need for improved filtering and verification processes in online recruitment channels to prevent exploitation.
Products Worth Considering

LG 34GX900A-B 34-Inch Ultragear OLED Curved Gaming Monitor – 3440 x 1440 WQHD, 240Hz, 0.03ms, NVIDIA G‑Sync, DisplayHDR True Black 400, HDMI

LG 27G810A-B 27-inch UltraGear 4K UHD IPS Gaming Monitor

LG UltraGear 27-inch QHD OLED Gaming Monitor, 240Hz, 0.03ms, G-SYNC Compatible, FreeSync Premium Pro, HDR True Black 400
As an affiliate, we earn on qualifying purchases.
Rise of Cyber Threats Exploiting Job Platforms
Over recent years, cybercriminals have increasingly targeted online job platforms, embedding malware or backdoors within job postings to compromise organizations. The recent detection of a backdoor in a LinkedIn offer aligns with this trend, which has seen a surge in malicious activity on professional networking sites.
Previous incidents include malware-laden resumes and phishing schemes aimed at harvesting credentials or deploying ransomware. Experts note that as online recruitment continues to grow, so does the sophistication of associated cyber threats, making vigilance essential for organizations of all sizes.
“The backdoor embedded in this LinkedIn job offer represents a significant escalation in recruitment-based cyber threats. It’s crucial for organizations to enhance their monitoring of online job postings.”
— an anonymous cybersecurity researcher
Details of the Backdoor’s Technical Mechanism
It is not yet clear how widespread this backdoor is or whether it has been exploited in active attacks. The full technical details of the embedded malicious code are still under analysis, and no confirmed cases of successful exploitation have been reported.
Further investigation is needed to determine if other similar backdoors exist in online job postings and how organizations can best detect and mitigate such threats.
Monitoring and Response Strategies for Organizations
Cybersecurity teams are expected to continue analyzing the backdoor’s technical aspects and monitor for related threats. Organizations should review their online recruitment processes, enhance detection capabilities, and educate hiring teams on spotting suspicious postings.
Further updates are anticipated as more details emerge about the scope and potential exploits of this backdoor, along with recommendations for mitigation.
Key Questions
What is a backdoor in a LinkedIn job offer?
A backdoor in a LinkedIn job offer refers to malicious code embedded within a job posting that could allow cybercriminals to gain unauthorized access to targeted systems once interacted with.
Has this backdoor been exploited yet?
There are no confirmed reports of active exploitation at this time, but cybersecurity analysts warn of the potential risk based on the detection of the malicious code.
How can organizations protect themselves from such threats?
Organizations should scrutinize online job postings, use advanced threat detection tools, and educate HR and IT teams about signs of malicious postings to prevent exploitation.
Is this threat limited to LinkedIn?
While this incident involves a LinkedIn job offer, similar tactics could be used on other online recruitment platforms, making vigilance across all channels important.
What should security leaders do now?
Security leaders should monitor emerging threats, review their detection protocols, and prepare response plans for potential exploitation of malicious job postings.
Source: IdeaNavigator AI